Grant Types
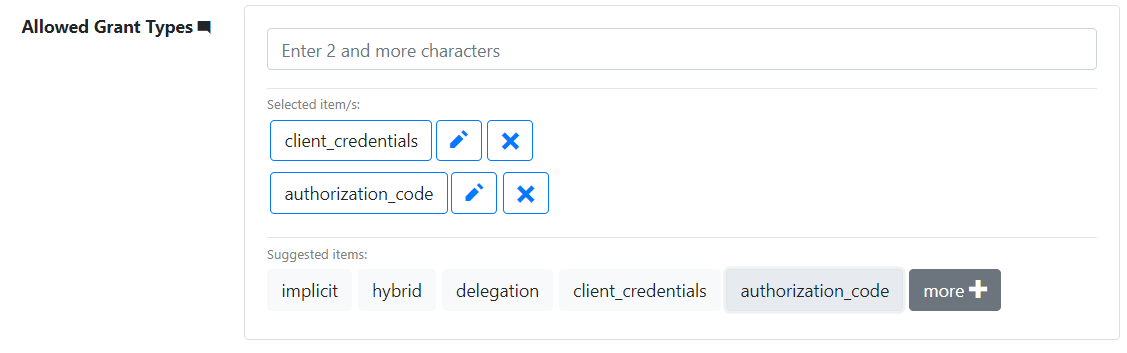
OAuth 2.0 defines several grant types, each suited for different use cases. The following grant types are supported in the Revelation helpdesk API and can be configured per client using the “Allowed Grant Types” field:
- Authorization Code Grant:
- Use Case: Web and mobile apps.
- Flow: The client application directs the user to the authorization server login page, which then returns an authorization code. The client exchanges this code for an access token.
- Pros: Highly secure because the access token is never exposed to the user agent.
- Implicit Grant:
- Use Case: Single-page applications (SPAs) and mobile apps.
- Flow: The client application directly receives the access token from the authorization server.
- Pros: Simplified flow, but less secure because the access token is exposed to the user agent.
- Client Credentials Grant:
- Use Case: Server-to-server communication.
- Flow: The client application uses its own credentials to obtain an access token.
- Pros: Suitable for applications that need to access resources without user involvement.
- Refresh Token Grant:
- Use Case: Extending the validity of an access token. Requires the “offline_access” scope to be added to the client.
- Flow: The client application uses a refresh token to obtain a new access token without user interaction.
- Pros: Improves user experience by reducing the need for repeated logins.